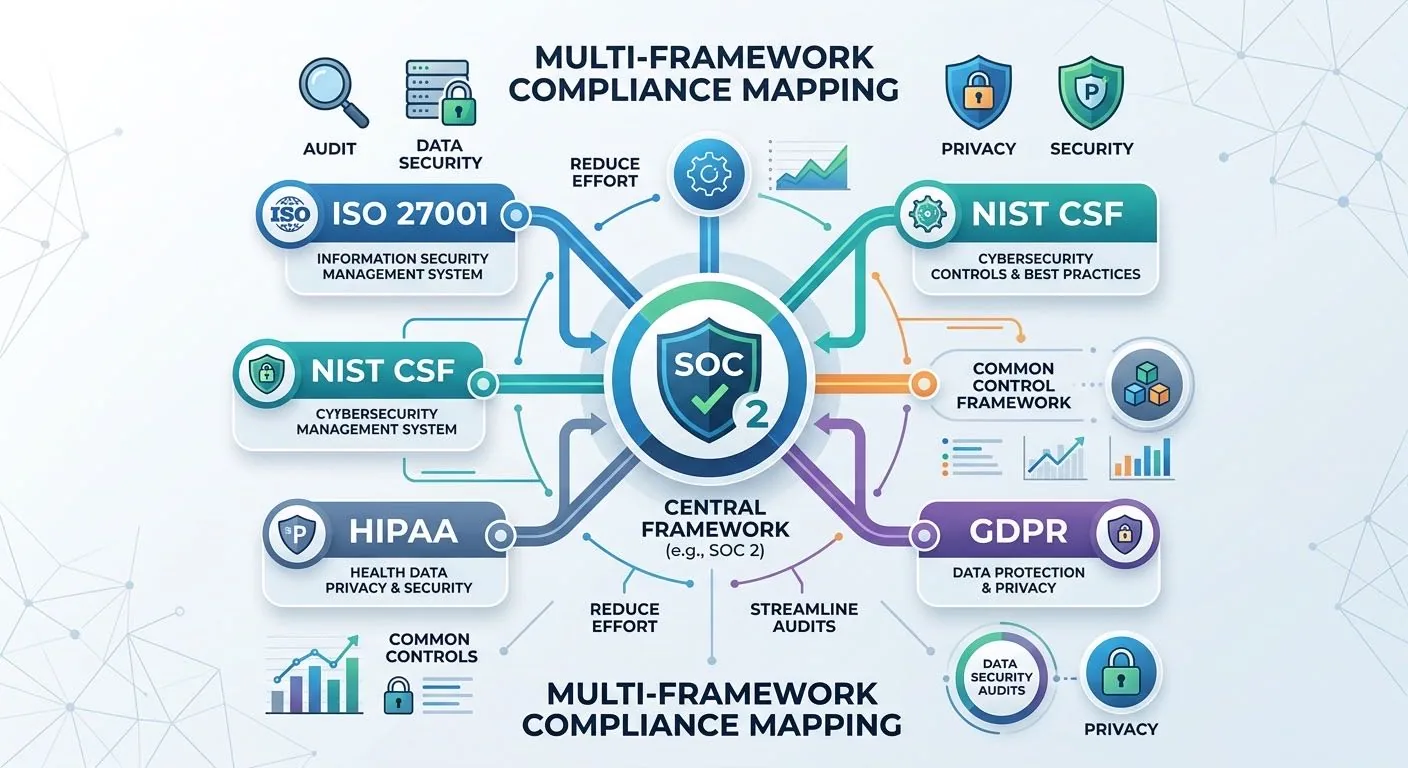
SOC 2 and Framework Mapping: Why 'One Audit, Multiple Frameworks' Is Now Standard
SOC 2 audits are increasingly built to double as evidence for CMMC, NIST, and ISO 27001 obligations at once, letting resource-constrained SMBs and MSPs satisfy multiple frameworks from a single audit cycle instead of paying for separate assessments.
READ MORE